[REVIEW] Enterprise AI Requirements 2026: A Practical Guide
Fig 1.0 · Visual representation of [review] enterprise ai requirements 2026: a practical guide
Enterprise AI Requirements 2026: Building Trustworthy Systems
A launch can pause when a team cannot reproduce a decision, prove a permission check, or show the audit trail that explains what happened. Until those pieces are clear, the system is not ready. Buyers are asking for auditability, reliability, and evidence before approval.
The Buyer's Checklist: AI Now Has Its Own Section
Start with the smallest production checklist first: measurable acceptance criteria, logging, permissions, failure handling, and versioned controls. Ask for those controls from the system owner. Verify the exact artifact that shows how the system was tested, what was logged, who can export it, and what happens if a required control fails. Confirm who reviews the logs, how long they are kept, and who approves the release.
For a small team, the must-have production artifacts are the acceptance criteria, test suite, log schema, permission matrix, rollback plan, and release gate record. The larger frameworks matter when a buyer, regulator, or contract asks for them. For example, ISO/IEC 42001 is a certifiable AI management system standard, so ask for the management-system artifacts that show how AI is governed. The CSA AI Controls Matrix v1.1 and AI-CAIQ are used for control review and questionnaire responses, so verify the completed control mappings, the control owner, the release review record, and the answers tied to the deployed system. SIG 2026 adds AI-lifecycle questions, so confirm evidence across data collection, training, deployment, and bias monitoring. SOC 2 can still support processing integrity questions, but buyers should not treat it as an AI-specific proof point.
For EU deployments, verify which obligations apply to the specific system, which deadline is relevant, and what evidence shows readiness for that deadline. The right question is not whether the vendor knows the regulation. The question is whether they can show the artifact that maps the system to it.
How to Make an AI System Ready for Production
Production readiness starts with acceptance tests, logging, permissions, and failure handling. If those are not defined before launch, the model is still in experiment mode. The build should answer what the system may do, what it may not do, what gets recorded, and what happens when a control fails.
Set risk and scope first, then write the acceptance criteria doc and the test suite before anyone treats the prompt as finished. From there, define the log schema, lock the permission matrix, and set the rollback plan and release gate together so the handoff is clear. In one support workflow, for example, engineering can own the evals, platform can own the logging shape, and the release manager can sign off only after the blocked-case test and rollback check both pass.
There should be one accountable owner per artifact. The deployment lead owns the acceptance criteria doc. Engineering owns the test suite. Platform or security owns the log schema. The system owner owns the permission matrix. The release manager owns the rollback plan. The pass condition is simple: each artifact exists, is versioned, and is reviewed before launch.
One worked example: the requirement is that a support workflow may summarize a case but cannot invent policy terms. The test sends a case with a missing policy field and expects the system to mark it unknown or route it for review. The failure is a response that fills the gap with a guess. The remediation is to update the fallback rule and re-run the eval. The approval record is the versioned test run that shows the failure was fixed and the release gate passed.
Write the Acceptance Criteria Before the Prompt
Start with measurable success criteria before prompt work begins. Define the test, the input, and what passing looks like. Use code-based checks for fast and repeatable validation, model-based checks when the task needs judgment, and human review when the output affects a real decision. Keep the eval set small enough to maintain, but drawn from real failures.
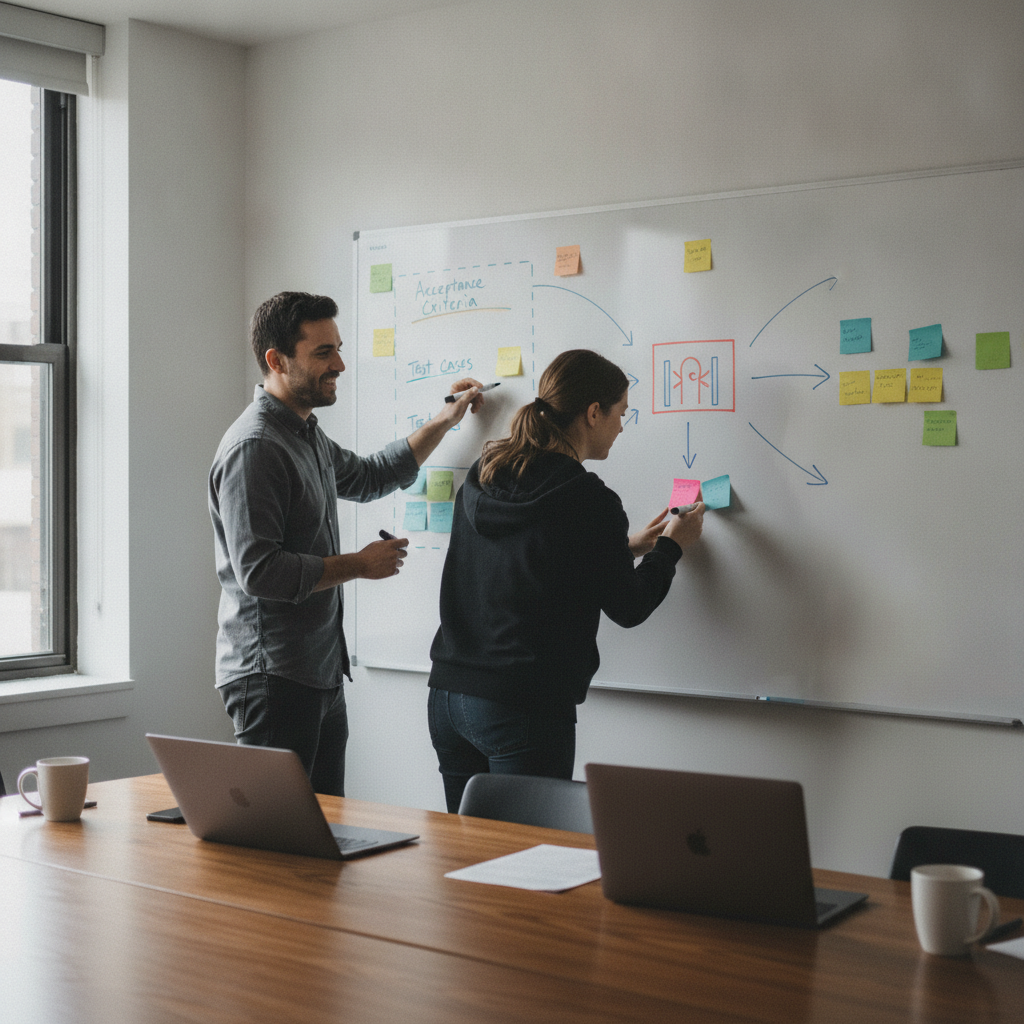
Capability evals tell you whether a system can do the job at all. Regression evals tell you whether it keeps doing it after a change. Human review is the last gate when the output affects a customer-facing decision or a material commitment. A release might pass capability and regression checks, but still stop if a reviewer sees a policy claim the system cannot prove.
A practical enterprise pattern is to keep the acceptance tests in the repo, run them on changes, and make the output of those tests part of release review. Keep the eval suite in the repo, assign ownership clearly, and use the agreed pass rate as the release gate. A sample release-gate decision might be: ship only if the capability eval passes, the regression eval stays green, and the human review finds no unsupported claims. A simple failure case is a customer asking for an answer the system cannot verify, or a prompt that omits a required field. Another failure case is a response that returns the right format but invents a fact.
Temperature 0 is Not a Guarantee, So Decide in Code
Temperature 0 can reduce variation, but it does not guarantee the same answer every time. That is why the business rule should live in code, not in the prompt. Put permissions, calculations, required facts, and customer-facing commitments in code with versioning. Use the model for bounded interpretation, not for the parts the buyer will hold you to.
Structured output can help by constraining the shape of the response. That means the system can be made to return valid JSON or a required field set, but it still does not prove the facts are right. In practice, the split looks like this: the model drafts a summary, the code validates required fields, permissions, and routing rules, and the release gate checks the versioned rule set. Before, the prompt tries to enforce who can see what and what counts as a valid answer. After, the code enforces those rules, the model fills in the bounded summary, and the release gate verifies the rule file, its version number, and the test that fails when the code rule is removed.
The operational owner should be able to point to the rule set, the version number, and the test that proves the business logic runs outside the model.
The Audit Trail Is a Product Feature
Auditability is not a side concern. It is part of the product. If the system cannot show what it did, who did it for, and which inputs it used, it is hard to review and hard to trust.
The operational workflow should be plain. Log the request ID, user or service account, tenant ID, timestamp, prompt version, model version, tool calls, input sources, output, refusal status, and audit-write result. Give the deployment owner and the security or compliance reviewer access to export the log. Keep the retention policy written down, with the period set by the system owner, the incident policy, the contract terms, and any applicable obligations. If the audit write fails, block the output, alert the on-call owner, and record the failure in the incident queue rather than letting the system continue silently.
Ask three things: what is logged, who can export it, and what happens when the log write fails. If those answers are unclear, the system is not ready for production.
Controls You Can Demonstrate, Not Describe
A control only matters if the buyer can reproduce it. If they cannot see the failure mode, it is still a claim.
The useful test is simple: can the team show the control, trigger the failure, and prove the system fails closed? For spend caps, the system should stop a request that exceeds the limit and log the block. For tool access, the system should reject a call from a role that lacks permission and show the denied attempt in the log. For prompt-injection defenses, the system should ignore a user instruction that tries to override policy, return a refusal, and keep the approved system behavior. For tenant boundaries, the system should not read or return data from another tenant, and the log should show the lookup was blocked.
A runnable test can look like this: send a request that asks for a restricted tool call, expect the call to fail, and expect a log entry with the request ID, denied tool, refusal status, and the owner who reviews the blocked request after escalation. Ask for the exact test case, the expected failure, and the log entry that proves the control worked.
Who Enterprise AI Requirements 2026 Is For
This checklist is for founders deciding whether to ship, small teams moving a prototype into production, and agencies or operators who are responsible for release risk.
It helps a founder with a prototype who needs senior technical review before the first release. It helps a small team replacing spreadsheets with a live workflow that needs code review and architecture help. It helps an agency or operator managing delivery risk that needs a tighter control set before production.
Not every AI feature needs enterprise governance. If the work can stay in spreadsheets, inboxes, or a simpler workflow, that is usually the better choice. The level of control should match customer impact, data sensitivity, external commitments, and the cost of failure. If the system does not need to make customer-facing decisions, or if the team cannot show how it will behave under review, AI may not be the right tool at all.
Honesty Is an Engineering Defect Class
Honesty is part of system design. If the model says it knows something it does not know, that is a defect. If it fills a gap with a guess, that is also a defect.
A clear example is this: if a system has no verified source for a fact, the test should require it to say that it does not have the data. The allowed outcomes are simple: stop, mark the field unknown in a template, or route to human review. The limitation is the absence of evidence. The test is whether the system refuses to invent an answer.
Ask for the rule, the refusal behavior, and the test that proves unsupported facts do not ship.
A Starting Checklist for an Enterprise AI Build
Start with the risk question. What will the system be allowed to do, and who owns the decision?
Then collect the evidence: acceptance criteria, test cases, logging rules, permission boundaries, and the release check that shows what happens when a control fails. If the system needs regulatory mapping, attach the exact standard or obligation to the artifact that proves readiness.
Before production, run a pre-production review, walk through the control map, and confirm that the logs, permissions, rollback plan, and fallback behavior are visible to the owner and the reviewer. If any of that is missing, the build is not ready. Request a pre-production AI readiness review from Practical Works, and we’ll walk through the control map, the release gate, and the evidence you need before launch. If the workflow still works better as a simpler process, say that too.
Frequently Asked Questions
What evidence should we ask for before launch?
Ask for the acceptance criteria doc, the test suite, the log schema, the permission matrix, the rollback plan, and the release gate record. The owner for each artifact should be named, and each artifact should be versioned.
Does EU applicability change the checklist?
Yes. Map the deployed system to the actual obligation, the market, and the use case. The useful proof is the artifact that shows which rule applies and why.
What happens if a required control fails?
The system should fail closed. That means blocking output, logging the failure, alerting the owner, and routing the issue through release review before it can ship.
How long should audit logs be kept?
Keep the retention policy written down and set the period to match the buyer’s recordkeeping needs, contract terms, incident policy, and applicable obligations. The key is that the period is explicit, approved, and tied to export access.
What vendor certifications matter here?
Treat certifications as part of the evidence set, not the whole answer. Ask for the artifact that shows how the deployed system was tested and controlled, plus the control mapping for the specific use case.